
Security that assumes the worst, so your team can relax.
Zero-trust access, managed detection and response, and audit-ready documentation, built into every Northgate environment rather than sold after a breach.
- 24/7 EDR monitoring
- HIPAA, SOC 2, CMMC mapping
- Zero-trust by default
Our approach
Assume breach, limit blast radius, prove it in an audit.
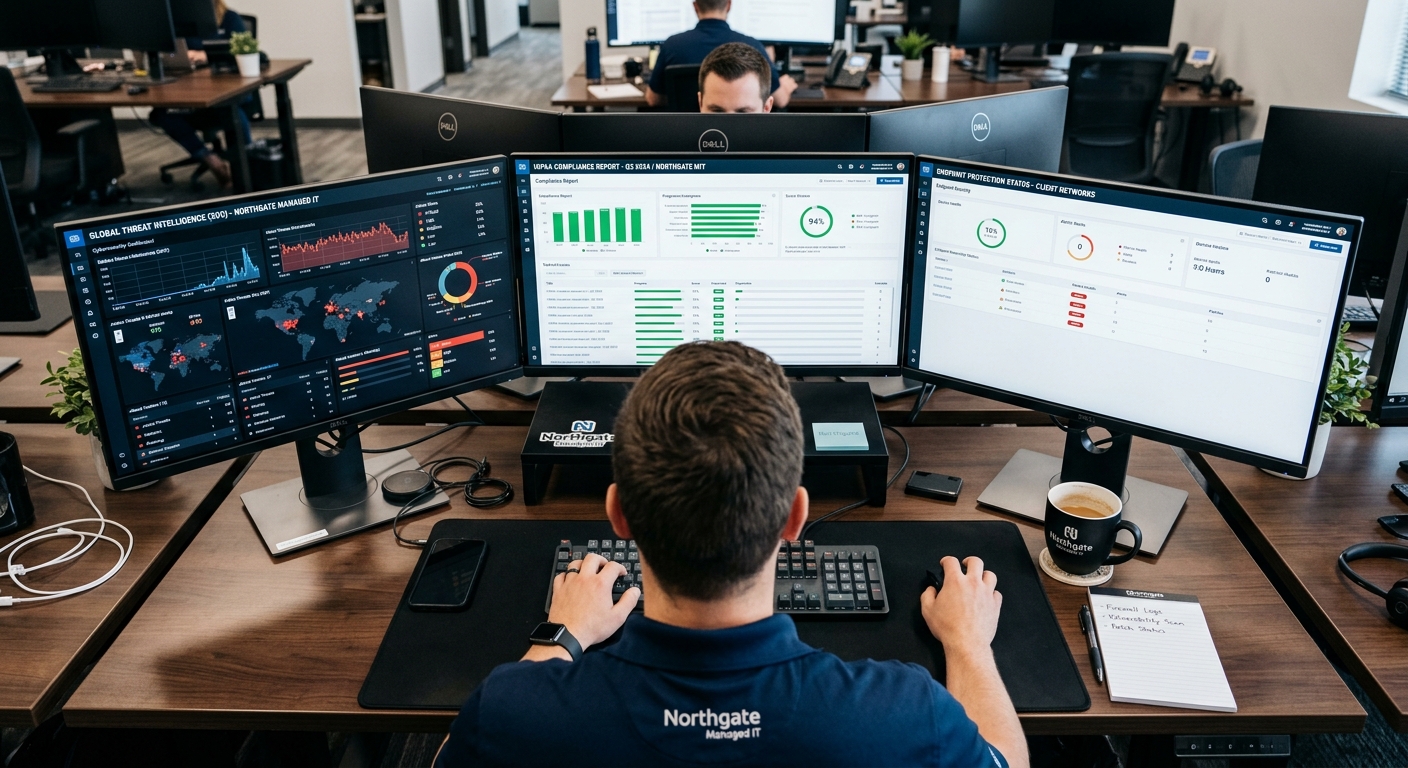
Modern attacks do not knock politely. They arrive through a reused password, a convincing email, or an unpatched laptop, and they move sideways once inside. Northgate designs every environment on zero-trust principles: verify every user and device, grant the least access needed, and monitor everything that moves. Endpoint detection and response runs around the clock so a compromised machine is isolated in minutes, not discovered in a forensic report weeks later. And because everything is documented as it is built, passing a HIPAA or SOC 2 audit becomes a matter of producing records you already have.
- Zero-trust access and multi-factor enforced across the environment
- 24/7 managed detection and response with rapid isolation
- Security awareness training that measurably lowers click rates
- Documentation mapped to HIPAA, SOC 2, and CMMC controls
How we protect your business

Endpoint detection & response
Every device monitored 24/7. Suspicious behavior triggers automatic isolation and a human investigation, fast.

Zero-trust access
Multi-factor everywhere, least-privilege by default, and conditional access that treats every login as unproven until verified.

Compliance mapping
Controls documented against HIPAA, SOC 2, and CMMC so an audit becomes paperwork you already have, not a fire drill.

Security awareness
Ongoing phishing simulations and training that turn your staff from the weakest link into a working line of defense.
Our incident response process
- 0124/7
Detect
Continuous monitoring across endpoints, identity, and network flags anomalous behavior the moment it appears.
- 02Minutes
Contain
A suspected compromise is automatically isolated from the rest of the environment, stopping lateral movement in minutes.
- 03Human
Investigate
Ohio-based engineers analyze the event, confirm scope, and eradicate the threat, keeping your leadership informed throughout.
- 04Improve
Harden
Every incident feeds back into your configuration and training, so the same door does not open twice.
Cybersecurity questions we hear often
We are small. Are we really a target?
Small and mid-sized businesses are targeted precisely because attackers assume the defenses are weaker. Automated attacks do not check your headcount first.Do we need this if we already have antivirus?
Traditional antivirus catches known threats after they run. Managed detection and response watches behavior and isolates threats that antivirus never recognizes.Can you help us pass an audit?
Yes. We document controls as we build, mapped to HIPAA, SOC 2, and CMMC, so audit season becomes a records request instead of a scramble.
Know where you stand
Start with a security assessment.
We will review your access, endpoints, and documentation, then show you the gaps in plain language and what it takes to close them.
